
こんにちは! JQです。
前回は『 OSS編~Fluented & Elasticseach & Kibana パート②~ 』 ということで、Fluented & ElasticseachとKibanaをインストールして実際にログ解析をしてみました。
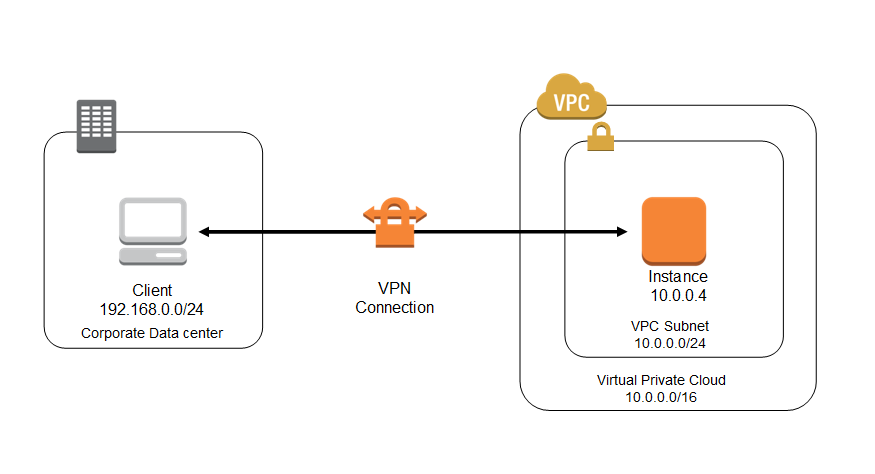
今回は『EC2編~OpenSwan&xl2tpdパート①~』と題して、EC2上でOpenSwan&xl2tpd を利用してL2TP/IPsecを構築してみたいと思います。
Openswan&xl2tpdのインストール
1. Openswan&xl2tpdのインストール
epelレポジトリを利用してyumコマンドでインストールを行います。
1[root@ ~]# sudo yum install --enablerepo=epel openswan xl2tpd2.各種設定
IPsecの設定を行います。
virtual_private=で許可するローカルIPを指定します。
また、includeも許可します。
1[root@ ~]# vim /etc/ipsec.conf23# /etc/ipsec.conf - Openswan IPsec configuration file45#67# Manual: ipsec.conf.589#1011# Please place your own config files in /etc/ipsec.d/ ending in .conf1213version 2.0 # conforms to second version of ipsec.conf specification1415# basic configuration1617config setup1819# Debug-logging controls: "none" for (almost) none, "all" for lots.2021# klipsdebug=none2223# plutodebug="control parsing"2425# For Red Hat Enterprise Linux and Fedora, leave protostack=netkey2627 protostack=netkey28 nat_traversal=yes29 virtual_private=%v4:10.0.0.0/8,%v4:192.168.0.0/16,%v4:172.16.0.0/1230 oe=off31 force_keepalive=yes32 keep_alive=603334# Enable this if you see "failed to find any available worker"3536# nhelpers=03738#You may put your configuration (.conf) file in the "/etc/ipsec.d/" and uncomment this.39include /etc/ipsec.d/*.confleftにインスタンスのローカルIP、leftnexthopにデフォルトゲートウェイを設定します。
1[root@ ~]# vim /etc/ipsec.d/l2tp-psk.conf2conn L2TP-PSK-NAT3 rightsubnet=vhost:%priv4 also=L2TP-PSK-noNAT5conn L2TP-PSK-noNAT6 authby=secret7 pfs=no8 auto=add9 keyingtries=310 rekey=no11 ikelifetime=8h12 keylife=1h13 type=transport14 left=[privateip]15 leftprotoport=17/170116 right=%any17 rightprotoport=17/018conn passthrough-for-non-l2tp19 type=passthrough20 left=[privateip]21 leftnexthop=[defaultgateway]22 right=0.0.0.023 rightsubnet=0.0.0.0/024 auto=route事前共有鍵の設定をします。
1[root@ ~]# vim /etc/ipsec.d/ipsec.secrets2%any: PSK "password"xl2tpdの設定を行います。
ip range にはリースするIPを記載します。
1[root@ ~]# cat /etc/xl2tpd/xl2tpd.conf2;3; This is a minimal sample xl2tpd configuration file for use4; with L2TP over IPsec.5;6; The idea is to provide an L2TP daemon to which remote Windows L2TP/IPsec7; clients connect. In this example, the internal (protected) network8; is 192.168.1.0/24. A special IP range within this network is reserved9; for the remote clients: 192.168.1.128/2510; (i.e. 192.168.1.128 ... 192.168.1.254)11;12; The listen-addr parameter can be used if you want to bind the L2TP daemon13; to a specific IP address instead of to all interfaces. For instance,14; you could bind it to the interface of the internal LAN (e.g. 192.168.1.9815; in the example below). Yet another IP address (local ip, e.g. 192.168.1.99)16; will be used by xl2tpd as its address on pppX interfaces.1718; IMPORTANT: always set listen-addr to a specific address, to work around a19; udpfromto bug!!!2021[global]22ipsec saref = yes2324; listen-addr = 192.168.1.9825;26; requires openswan-2.5.18 or higher - Also does not yet work in combination27; with kernel mode l2tp as present in linux 2.6.23+28; ipsec saref = yes29; Use refinfo of 22 if using an SAref kernel patch based on openswan 2.6.35 or30; when using any of the SAref kernel patches for kernels up to 2.6.35.31; ipsec refinfo = 3032;33; force userspace = yes34;35; debug tunnel = yes3637[lns default]38ip range = xxx.xxx.xxx.xxx-xxx.xxx.xxx.yyy39local ip = [privateip]40; leave chap unspecified for maximum compatibility with windows, iOS, etc41; require chap = yes42refuse pap = yes43require authentication = yes44name = LinuxVPNserver45ppp debug = yes46pppoptfile = /etc/ppp/options.xl2tpd47length bit = yesログ設定やDNS設定を記載します。
1[root@ ~]# vim /etc/ppp/options.xl2tpd2ipcp-accept-local3ipcp-accept-remote4ms-dns 8.8.8.856# ms-dns 192.168.1.178# ms-dns 192.168.1.3910# ms-wins 192.168.1.21112# ms-wins 192.168.1.41314noccp15auth16crtscts17idle 180018mtu 141019mru 141020nodefaultroute21debug22lock23proxyarp24connect-delay 50002526refuse-pap27refuse-chap28refuse-mschap29require-mschap-v230logfile /var/log/xl2tpd.l2tp-ipsec.log3132# To allow authentication against a Windows domain EXAMPLE, and require the3334# user to be in a group "VPN Users". Requires the samba-winbind package3536# require-mschap-v23738# plugin winbind.so3940# ntlm_auth-helper '/usr/bin/ntlm_auth --helper-protocol=ntlm-server-1 --require-membership-of="EXAMPLE\\VPN Users"'4142# You need to join the domain on the server, for example using samba:4344# http://rootmanager.com/ubuntu-ipsec-l2tp-windows-domain-auth/setting-up-openswan-xl2tpd-with-native-windows-clients-lucid.htmlユーザーとパスワードを設定します。
1[root@ ~]# vim /etc/ppp/chap-secrets23# Secrets for authentication using CHAP45# client server secret IP addresses67user * password *サービスを再起動して設定を反映させます。
1[root@ ~]# /etc/rc.d/init.d/ipsec start2ipsec_setup: Starting Openswan IPsec U2.6.37/K3.4.62-53.42.amzn1.x86_64...3[root@ ~]# /etc/rc.d/init.d/xl2tpd start4Starting xl2tpd: [ OK ]3.SecurityGroupの開放
SecurityGroupで以下ポートを開放します。
500:udp
4500:udp
1701:udp
今回はここまでとなります。
いかがでしたでしょうか?
次回は『EC2編~OpenSwan&xl2tpdパート②~』ということで、Windowsの標準クライアントを利用して実際にVPNで接続してみたいと思います。
お楽しみに!
——————————————————————————————————
ナレコムクラウドのFacebookに『いいね!』をクリックして頂くと
最新のお役立ちレシピが配信されます★
——————————————————————————————————

