
こんにちは!Tamaです!
前回は『 AWS CLIとCloudFormationでVPCを作ってEC2を立ち上げてみた①~AWS CLI編~ 』と題して、AWS CLIを用いVPC内にEC2インストールを立ち上げました。
CloudFormationからのデプロイ
今回も一括デプロイサービスであるCloudFormationをAWS CLIでの構築と比較するため、CloudFormationを使ってVPCの作成とEC2インスタンスの立ち上げを一括で行います。
今回作成する環境は前回と同じで下の表になります。
| OS | Amazon Linux AMI 2015.03.0 x86_64 HVM GP2 |
| AMI | ami-cbf90ecb |
| Instance Type | t2.micro |
| Root Volume | 8GiB |
| VPC IP Range | 10.0.0.0/16 |
| Subnet IP Range | 10.0.0.0/24 |
| SecurityGroup | SSH(port:22) source:0.0.0.0/0 |
| New Key Pair | NO |
- テンプレートを用意します。
今回は「A single Amazon EC2 in an Amazon VPC」テンプレートを今回の構成に合わせて書き直したものを用いました。全文はページ下部にあります。
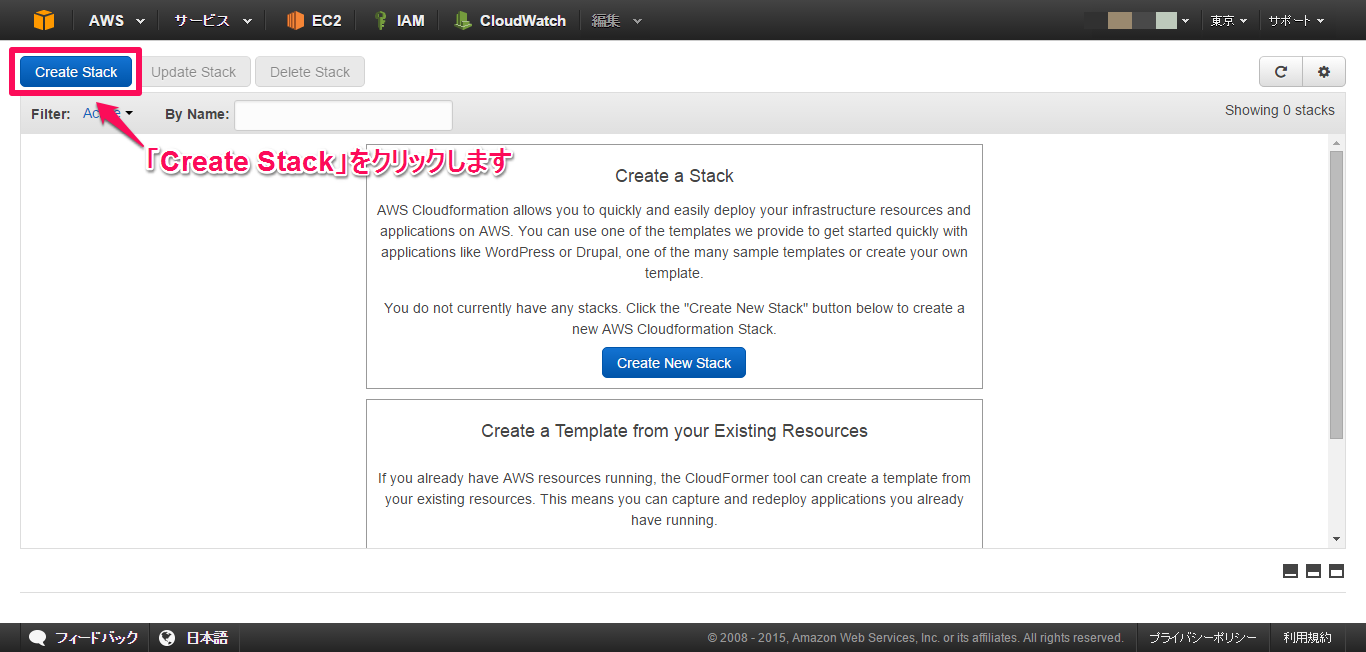
- ManagementConsoleのサービス一覧からCloudFormationを選択します。
- 「Create Stack」をクリックします。
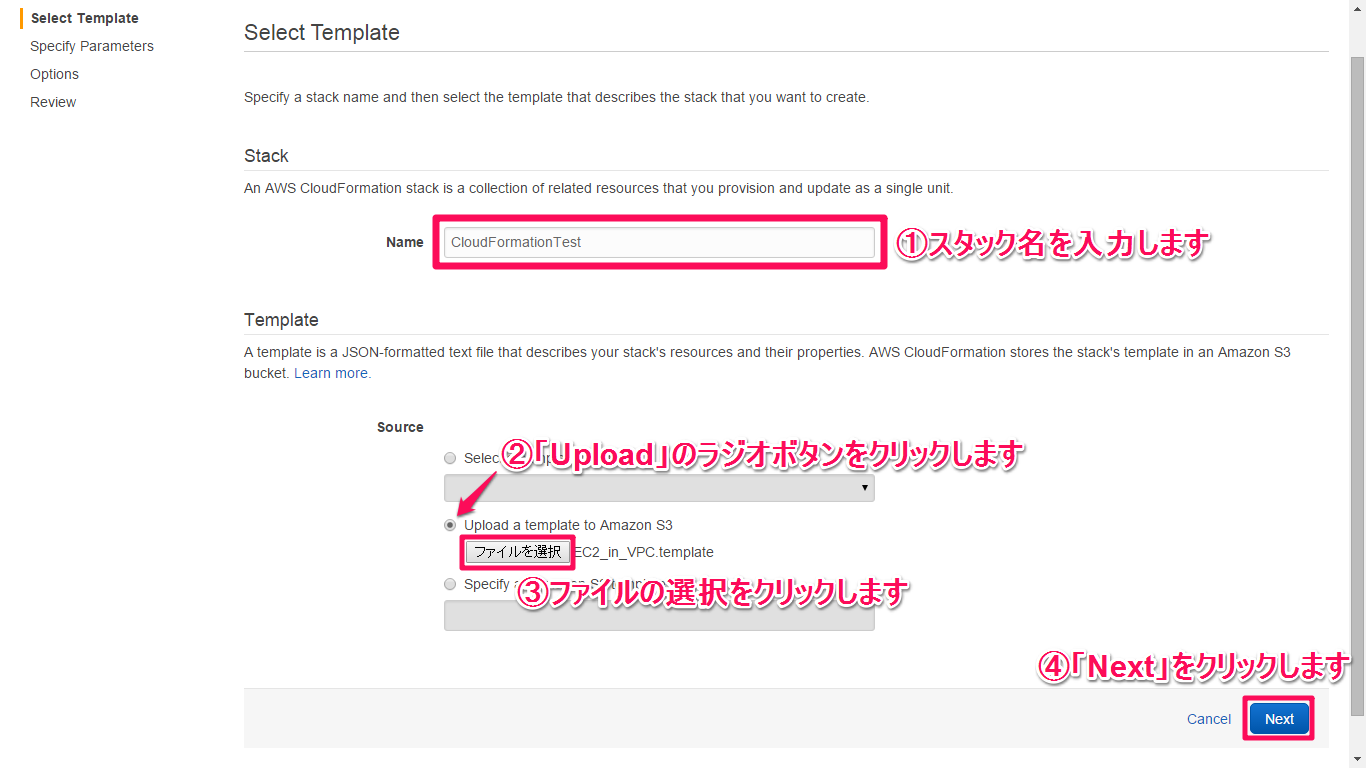
- スタック名を入力し、使用するテンプレートファイルをアップロードします。
サンプルとしてAWSから提供されているもの、S3にアップロードされ公開されているものを選択することもできます。
(サンプルテンプレートは下記URLにあります。)
http://docs.aws.amazon.com/AWSCloudFormation/latest/UserGuide/cfn-sample-templates.html
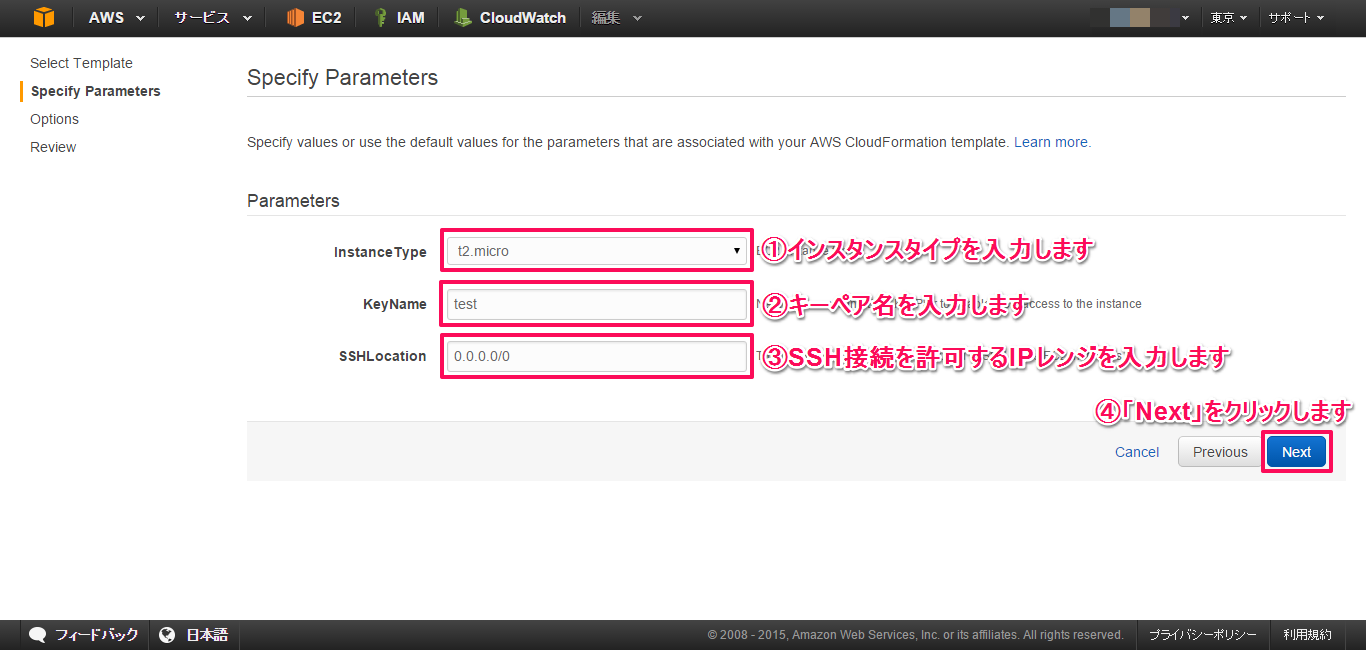
- 構成に合わせてパラメータを入力します。
今回の構成ではt2.microインスタンス、キーペアは予め作ったもの、IPレンジは0.0.0.0/0を入力しました。
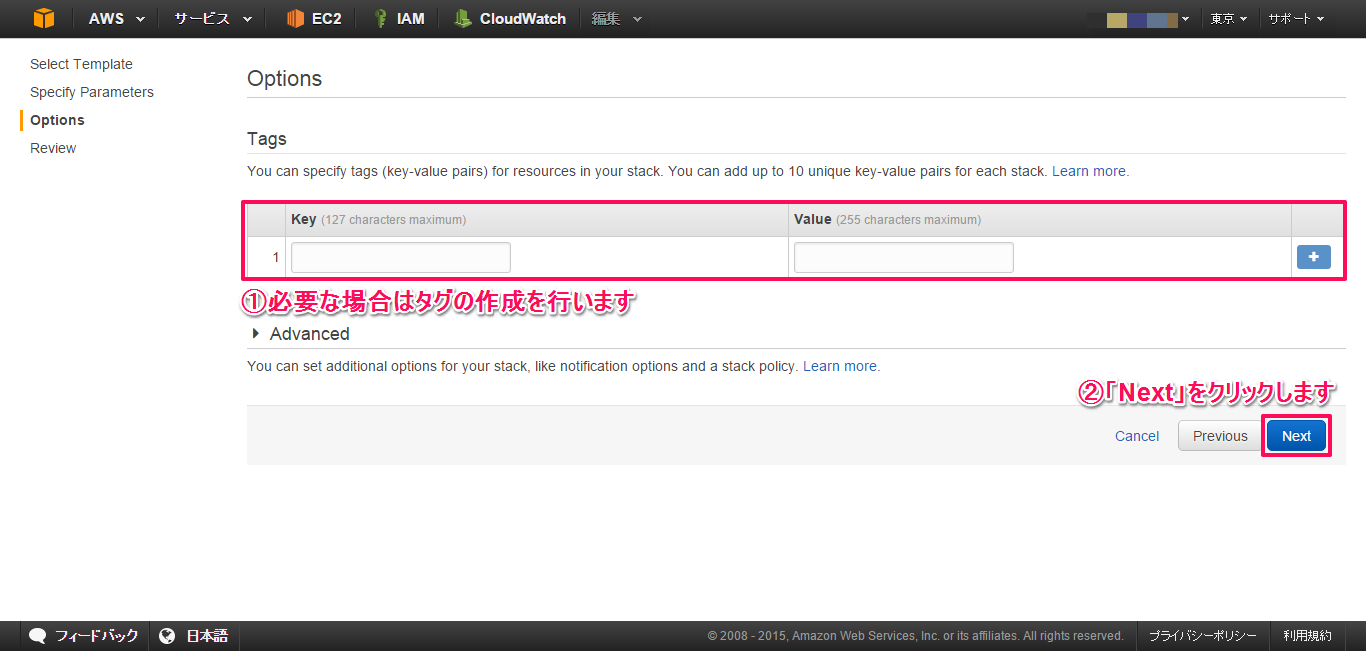
- 最後にネームタグなどタグが必要な場合は作成します。
- 内容を確認し「Create」をクリックします。
1. Statusが「CREATE
INPROGRESS」から「CREATE_COMPLETE」になると構築完了です。
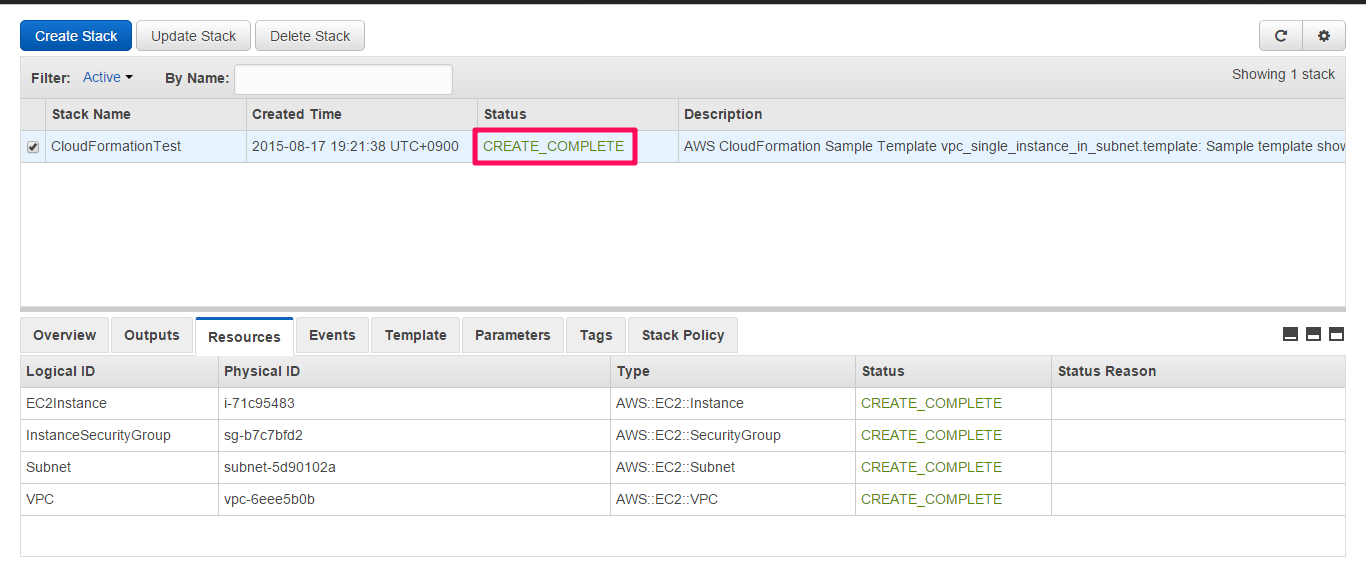
CloudFormationでのVPCとEC2インスタンスの立ち上げは以上になります。
お疲れさまでした!
CloudFormationでは前の工程を待ってデプロイしてくれるのでミスも無く便利ですね。
次回はAWS CLIとCloudFormationの利点と特徴を考えていきます。
またお会いしましょう!
今回使用したテンプレートは以下になります。
サンプルテンプレートを編集したものです。
1template2----------------------------------------------------------------------------------3{4 "AWSTemplateFormatVersion" : "2010-09-09",56 "Description" : "AWS CloudFormation Test Template vpc_single_instance_in_subnet.template: Create a VPC and add an EC2 instance with a security group. ",78 "Parameters" : {9 "InstanceType" : {10 "Description" : "EC2 instance type",11 "Type" : "String",12 "Default" : "t2.micro",1314 "AllowedValues" : [ "t1.micro","t2.micro","m1.small","m1.medium","m1.large","m1.xlarge","m2.xlarge","m2.2xlarge","m2.4xlarge","m3.xlarge","m3.2xlarge","c1.medium","c1.xlarge","cc1.4xlarge","cc2.8xlarge","cg1.4xlarge"],15 "ConstraintDescription" : "must be a valid EC2 instance type."16 },17 "KeyName": {18 "Description" : "Name of an existing EC2 KeyPair to enable SSH access to the instance",19 "Type": "String",20 "MinLength": "1",21 "MaxLength": "255",22 "AllowedPattern" : "[\\x20-\\x7E]*",23 "ConstraintDescription" : "can contain only ASCII characters."24 },25 "SSHLocation" : {26 "Description" : " The IP address range that can be used to SSH to the EC2 instances",27 "Type": "String",28 "MinLength": "9",29 "MaxLength": "18",30 "Default": "0.0.0.0/0",31 "AllowedPattern": "(\\d{1,3})\\.(\\d{1,3})\\.(\\d{1,3})\\.(\\d{1,3})/(\\d{1,2})",32 "ConstraintDescription": "must be a valid IP CIDR range of the form x.x.x.x/x."33 }34 },35 "Resources" : {36 "VPC" : {37 "Type" : "AWS::EC2::VPC",38 "Properties" : {39 "CidrBlock" : "10.0.0.0/16",40 "Tags" : [ {"Key" : "Application", "Value" : { "Ref" : "AWS::StackId"} } ]41 }42 },43 "Subnet" : {44 "Type" : "AWS::EC2::Subnet",45 "Properties" : {46 "VpcId" : { "Ref" : "VPC" },47 "CidrBlock" : "10.0.0.0/24",48 "MapPublicIpOnLaunch" : "True",49 "Tags" : [ {"Key" : "Application", "Value" : { "Ref" : "AWS::StackId"} } ]50 }51 },52 "InternetGateway" : {53 "Type" : "AWS::EC2::InternetGateway",54 "Properties" : {55 "Tags" : [ {"Key" : "Application", "Value" : { "Ref" : "AWS::StackId"} } ]56 }57 },58 "AttachGateway" : {59 "Type" : "AWS::EC2::VPCGatewayAttachment",60 "Properties" : {61 "VpcId" : { "Ref" : "VPC" },62 "InternetGatewayId" : { "Ref" : "InternetGateway" }63 }64 },65 "RouteTable" : {66 "Type" : "AWS::EC2::RouteTable",67 "Properties" : {68 "VpcId" : {"Ref" : "VPC"},69 "Tags" : [ {"Key" : "Application", "Value" : { "Ref" : "AWS::StackId"} } ]70 }71 },72 "Route" : {73 "Type" : "AWS::EC2::Route",74 "DependsOn" : "AttachGateway",75 "Properties" : {76 "RouteTableId" : { "Ref" : "RouteTable" },77 "DestinationCidrBlock" : "0.0.0.0/0",78 "GatewayId" : { "Ref" : "InternetGateway" }79 }80 },81 "SubnetRouteTableAssociation" : {82 "Type" : "AWS::EC2::SubnetRouteTableAssociation",83 "Properties" : {84 "SubnetId" : { "Ref" : "Subnet" },85 "RouteTableId" : { "Ref" : "RouteTable" }86 }87 },88 "NetworkAcl" : {89 "Type" : "AWS::EC2::NetworkAcl",90 "Properties" : {91 "VpcId" : {"Ref" : "VPC"},92 "Tags" : [ {"Key" : "Application", "Value" : { "Ref" : "AWS::StackId"} } ]93 }94 },95 "InboundNetworkAclEntry" : {96 "Type" : "AWS::EC2::NetworkAclEntry",97 "Properties" : {98 "NetworkAclId" : {"Ref" : "NetworkAcl"},99 "RuleNumber" : "100",100 "Protocol" : "-1",101 "RuleAction" : "allow",102 "Egress" : "false",103 "CidrBlock" : "0.0.0.0/0"104 }105 },106 "OutBoundNetworkAclEntry" : {107 "Type" : "AWS::EC2::NetworkAclEntry",108 "Properties" : {109 "NetworkAclId" : {"Ref" : "NetworkAcl"},110 "RuleNumber" : "100",111 "Protocol" : "-1",112 "RuleAction" : "allow",113 "Egress" : "true",114 "CidrBlock" : "0.0.0.0/0"115 }116 },117 "SubnetNetworkAclAssociation" : {118 "Type" : "AWS::EC2::SubnetNetworkAclAssociation",119 "Properties" : {120 "SubnetId" : { "Ref" : "Subnet" },121 "NetworkAclId" : { "Ref" : "NetworkAcl" }122 }123 },124 "InstanceSecurityGroup" : {125 "Type" : "AWS::EC2::SecurityGroup",126 "Properties" : {127 "VpcId" : { "Ref" : "VPC" },128 "GroupDescription" : "Enable SSH access via port 22",129 "SecurityGroupIngress" : [130 {"IpProtocol" : "tcp", "FromPort" : "22", "ToPort" : "22", "CidrIp" : { "Ref" : "SSHLocation"}}131 ]132 }133 },134 "EC2Instance" : {135 "Type" : "AWS::EC2::Instance",136 "Properties" : {137 "ImageId" : "ami-cbf90ecb",138 "SecurityGroupIds" : [{ "Ref" : "InstanceSecurityGroup" }],139 "SubnetId" : { "Ref" : "Subnet" },140 "InstanceType" : { "Ref" : "InstanceType" },141 "KeyName" : { "Ref" : "KeyName" },142 "Tags" : [ { "Key" : "Application", "Value" : "string" } ]143 }144 }145 }146}147----------------------------------------------------------------------------------
